How the GEET $1000 Amazon Gift Card Exploit Hijacks Mobile Phones
Security experts break down the clever scripts, bypass tactics, and history-hijacking tricks behind the GEET mobile redirect scam.

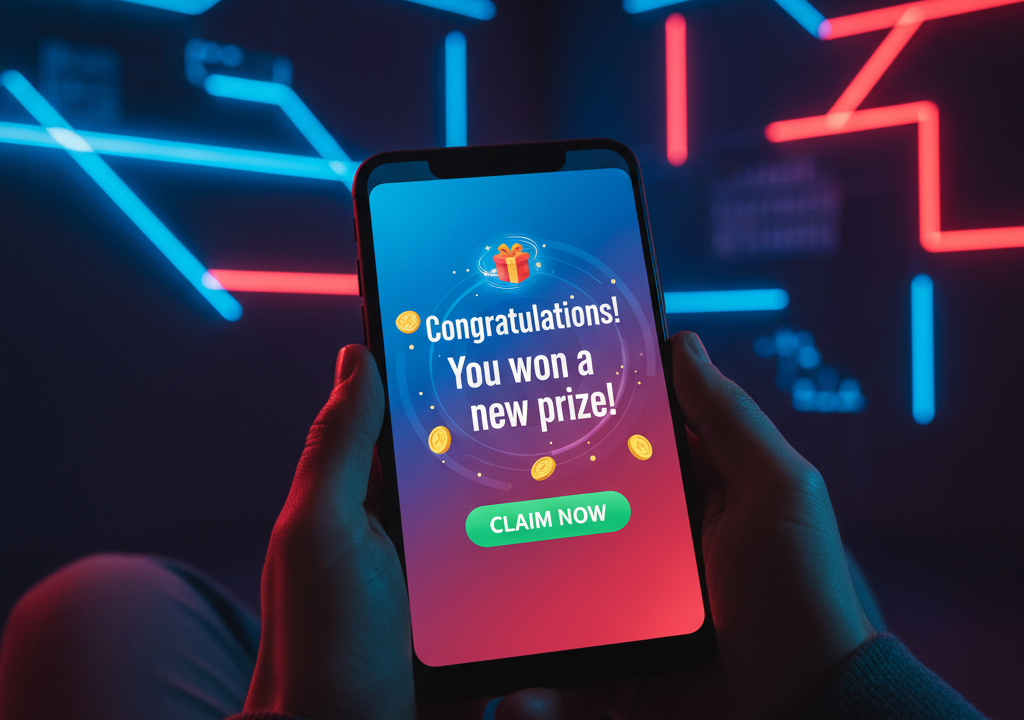
You are browsing a favorite blog on your phone. The page loads normally, but then the screen suddenly goes white. A second later, a flashy alert takes over your browser. “Congratulations, Amazon User!” it screams, promising a $1,000 gift card. If you try to tap your phone’s back button, the browser refuses to leave. You are trapped.
This is the classic GEET mobile redirect exploit. It has plagued mobile browsers for months. Security researchers have finally mapped out exactly how this sophisticated malvertising scheme hijacks devices without the user clicking a single link.
The Anatomy of a Hijack
Security analysts say the attack is remarkably stealthy. Unlike old-school pop-ups, GEET does not rely on sketchy downloads or compromised apps. Instead, it exploits the complicated, automated systems that run online advertising.
It all starts behind the scenes of mainstream web design. When you visit a website, the publisher’s ad spaces are sold in milliseconds via real-time bidding. Malicious actors hide their redirect scripts inside legitimate-looking ad creatives. Once a rogue ad wins a spot on a high-traffic site, the trap is set. The moment your mobile browser renders the ad, the malicious JavaScript executes automatically. No clicks are required to set it off.
The Tech Behind the Trap
The GEET code is incredibly smart. More importantly, it knows how to hide. Before it redirects anyone, the script runs a series of quick background checks on your device.
It looks at your screen resolution, your phone’s battery level, and even how you hold the device. The goal? To make sure you are a real person on a physical mobile phone, not an automated security scanner trying to catch malicious code. If the script detects a virtual machine or a desktop browser, it goes dark. It behaves like a normal, boring advertisement. This evasion makes it incredibly difficult for ad networks to spot and ban.
Breaking the Back Button
If the script decides you are a real mobile user, the hijack begins. It does not send you straight to the fake Amazon page. That would be too easy for security systems to track and block. Instead, it bounces your browser through a rapid succession of middleman domains.
These intermediary sites act as traffic directors, obscuring the source of the attack. By the time you reach the final landing page, your browser has jumped through three or four different servers across the globe.
What makes GEET particularly frustrating is its absolute refusal to let you leave. Have you ever tried to hit “back” only to find yourself stuck on the same scam page? That is a deliberate technique called history manipulation.
The script uses basic web APIs to flood your browser’s history with copies of the scam URL. When you tap back, you simply navigate to the previous entry in the fake history chain, leaving you trapped in an endless loop on the page.
The Phishing Endgame
Once trapped, the user is prompted to answer a quick survey to claim their $1,000 Amazon gift card. But there is no gift card. Instead, the survey asks for sensitive information: credit card details to cover a minor “shipping fee,” your home address, or your Social Security number. It is a highly effective, high-volume phishing funnel.
How to Protect Yourself
For everyday mobile users, the best defense is simple but hard to remember in the heat of the moment. Do not tap anything on the screen. Do not try to close the pop-up using its own “X” button, as that often triggers another redirect loop.
Instead, close the entire browser tab immediately. If the redirect loop persists when you reopen your browser, you may need to go into your phone’s settings and clear your browser cache entirely.
Web publishers face a much harder fight. Because these rogue ads slip through reputable ad exchanges, blocking them requires active monitoring. Security firms recommend that websites implement strong Content Security Policies (CSP). These policies act as digital bouncers, telling the browser exactly which domains are allowed to run scripts on the site. If an ad tries to redirect a user to an unauthorized domain, the browser blocks the action on the spot.
Ultimately, the GEET campaign highlights a massive vulnerability in the modern mobile web. As long as ad networks rely on automated bidding with loose screening, clever scammers will find ways to hijack our screens. Until those loopholes close, stay vigilant, and remember: no one is handing out free thousand-dollar gift cards.